Scanning Images from AWS ECR
Configure RAD Security to scan container images from Amazon Elastic Container Registry
The rad-sbom plugin generates an SBOM (Software Bill of Materials) for every container image running in your cluster. It downloads images directly from registry APIs, so it needs credentials for private registries.
ECR uses short-lived 12-hour tokens, so rad-sbom cannot use standard imagePullSecrets. Instead, an IAM role with the necessary permissions must be attached to the service account named rad-sbom.
Configuring Authentication for ECR
There are two approaches to configure authentication:
- EKS Pod Identity - AWS documentation
- IRSA - AWS documentation
IAM Policy
Create an IAM policy with the following permissions:
{
  "Version": "2012-10-17",
  "Statement": [
    {
      "Effect": "Allow",
      "Action": [
        "ecr:DescribeImageScanFindings",
        "ecr:GetLifecyclePolicyPreview",
        "ecr:GetDownloadUrlForLayer",
        "ecr:DescribeImageReplicationStatus",
        "ecr:ListTagsForResource",
        "ecr:ListImages",
        "ecr:BatchGetRepositoryScanningConfiguration",
        "ecr:BatchGetImage",
        "ecr:DescribeImages",
        "ecr:DescribeRepositories",
        "ecr:BatchCheckLayerAvailability",
        "ecr:GetRepositoryPolicy",
        "ecr:GetLifecyclePolicy",
        "ecr:GetAuthorizationToken"
      ],
      "Resource": "*"
    }
  ]
}
EKS Pod Identity
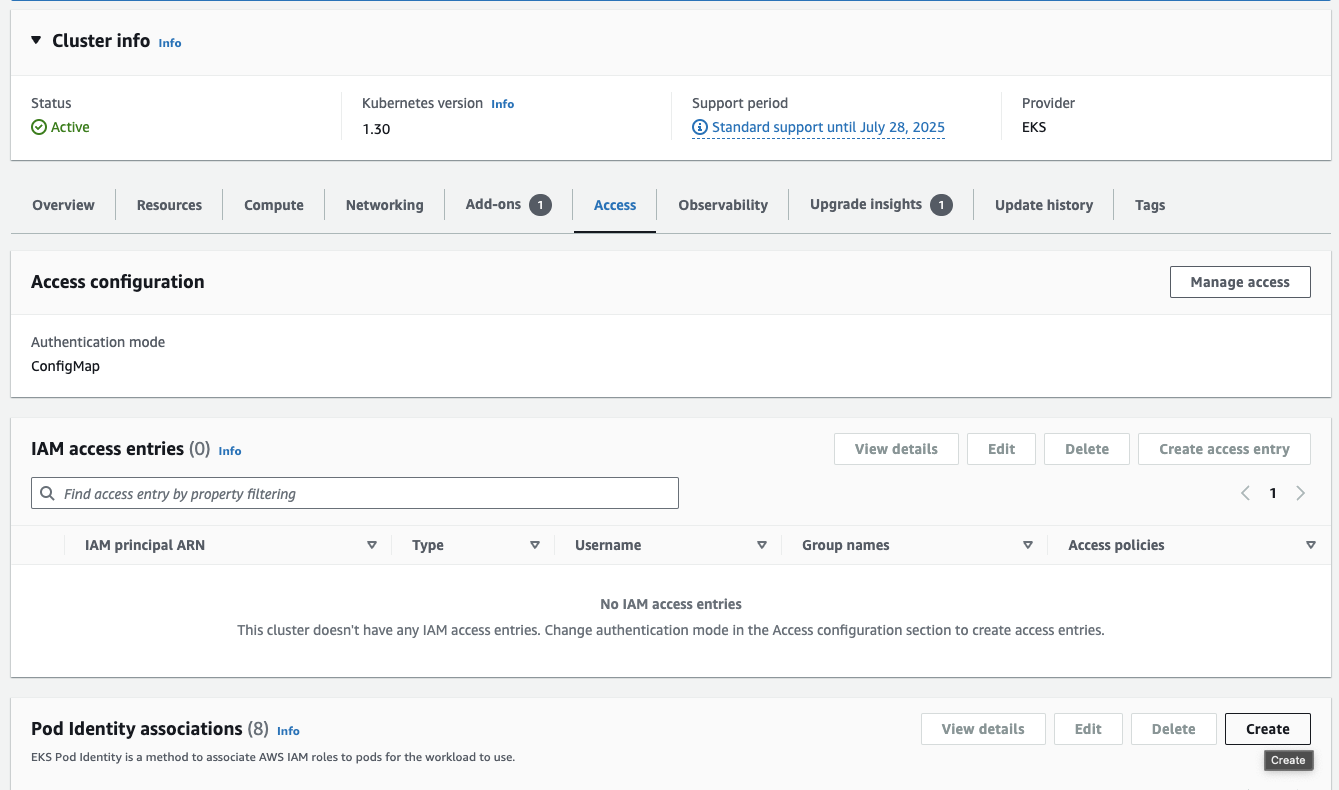
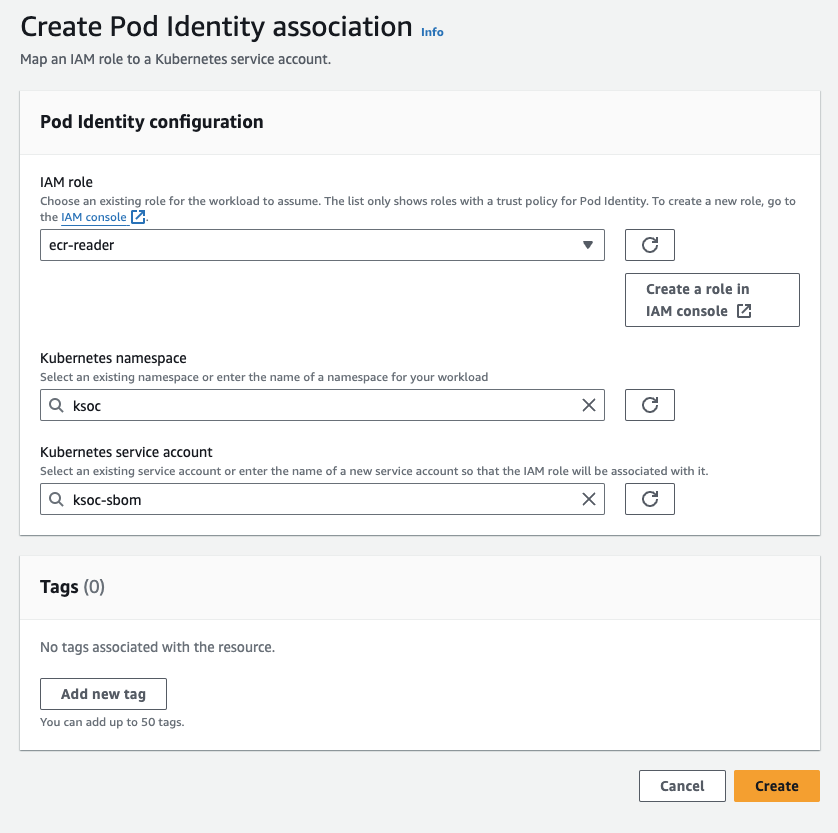
Create a Pod Identity Association for the rad-sbom service account:
IRSA
If using IRSA instead of EKS Pod Identity, add the following annotation to your values.yaml:
sbom:
  serviceAccountAnnotations:
    eks.amazonaws.com/role-arn: <IAM_ROLE_ARN>